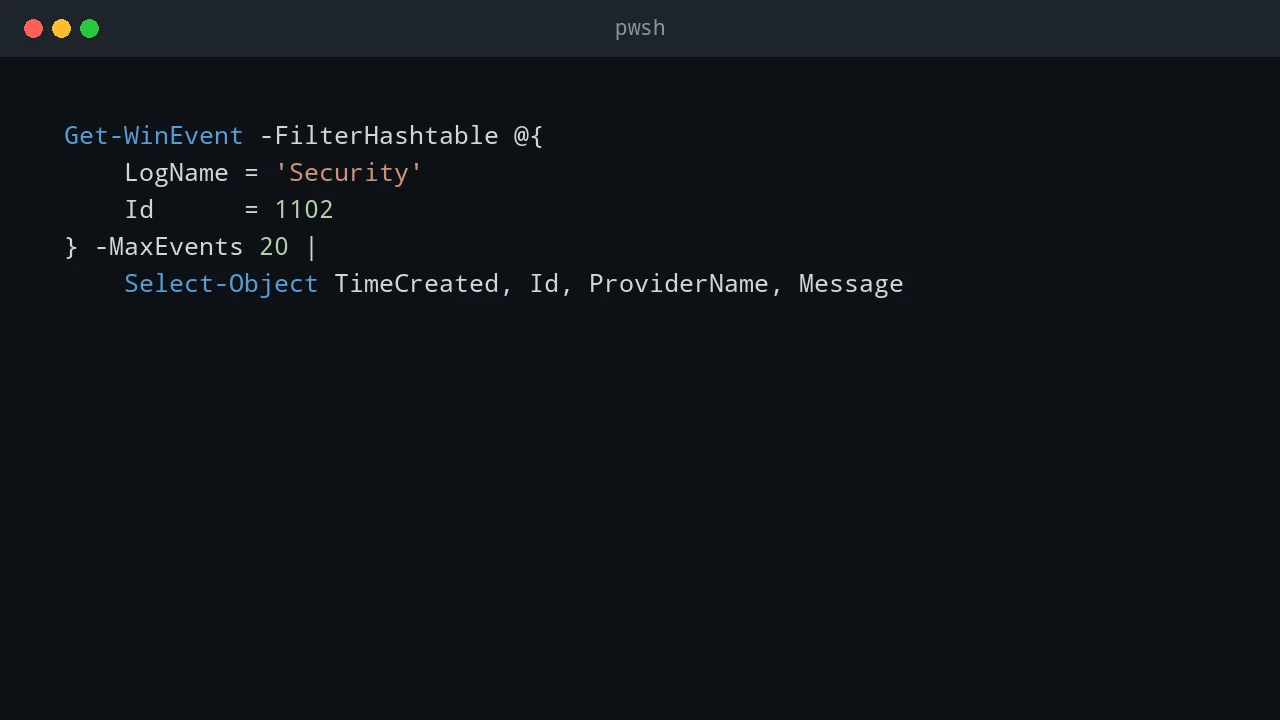
Windows Event Log Tampering: What Admins Should Defend Against
Defensive notes on Windows event log tampering, audit risk, detection signals, and practical controls for administrators.
Defensive notes on Windows event log tampering, audit risk, detection signals, and practical controls for administrators.
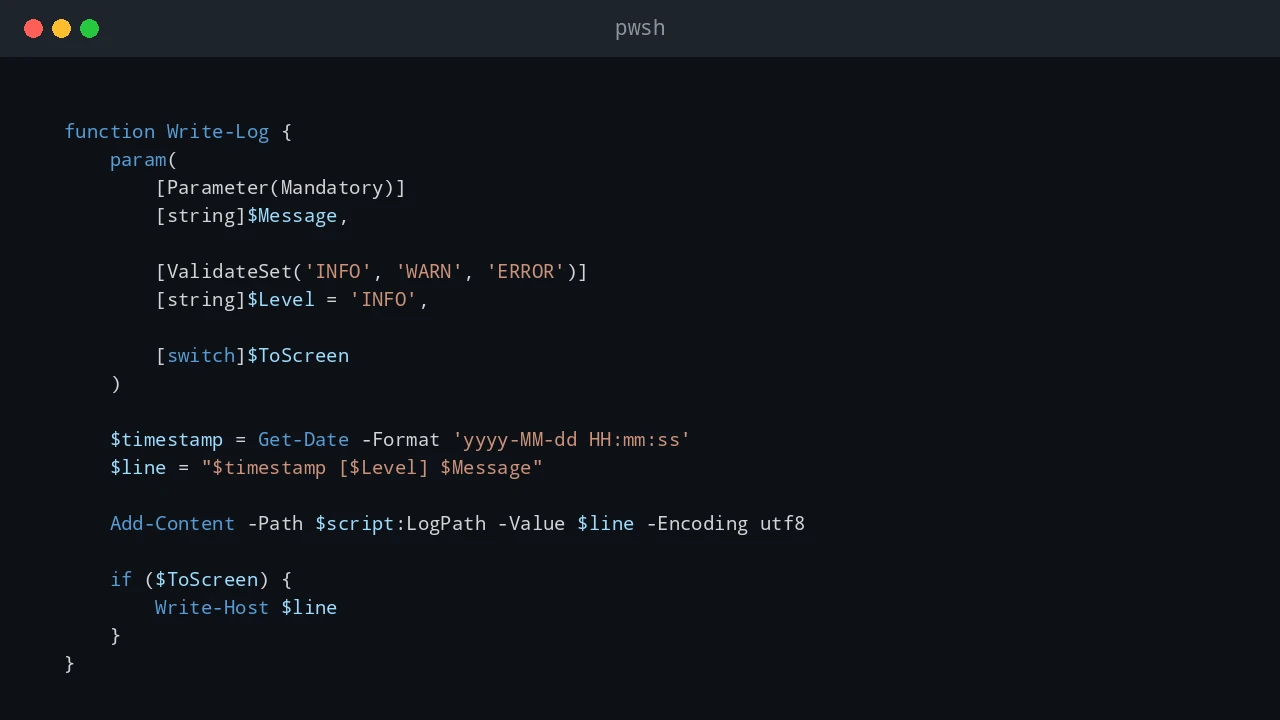
Practical logging patterns for PowerShell scripts that run unattended in scheduled tasks, servers, and admin automation.
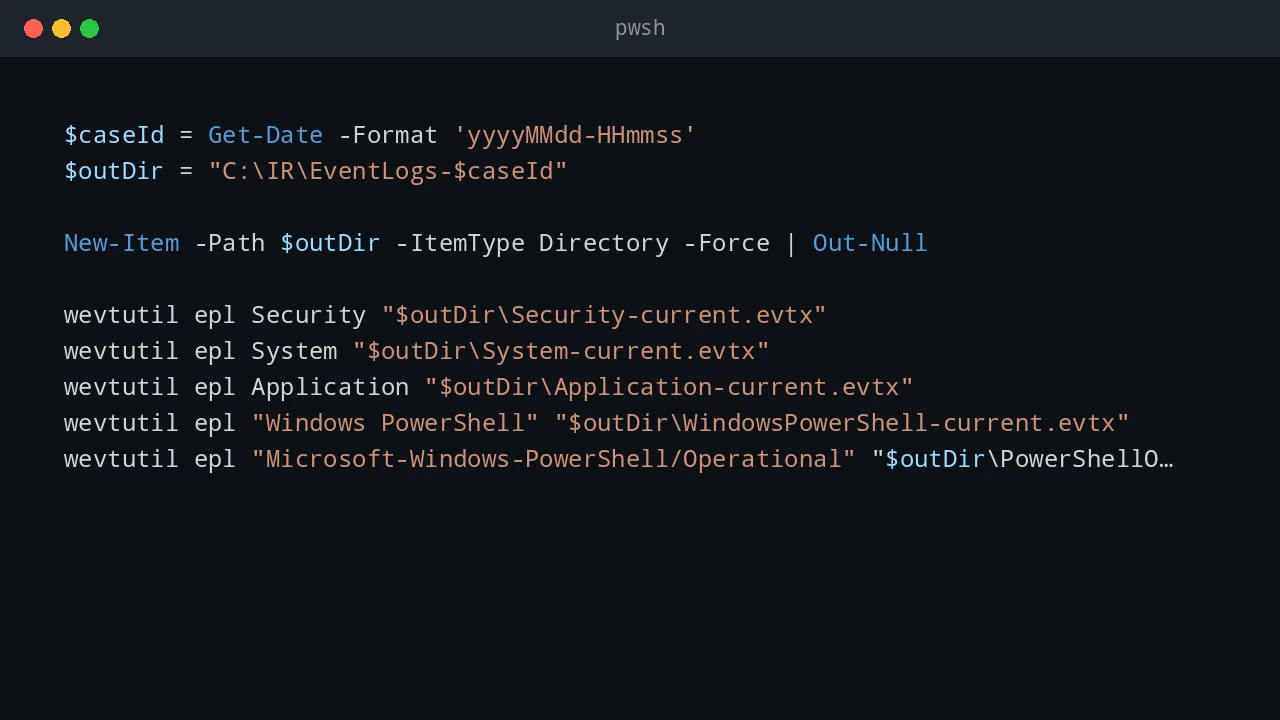
What administrators can recover after Windows event logs are cleared, and how to prevent local log loss with forwarding, exports, and central collection.
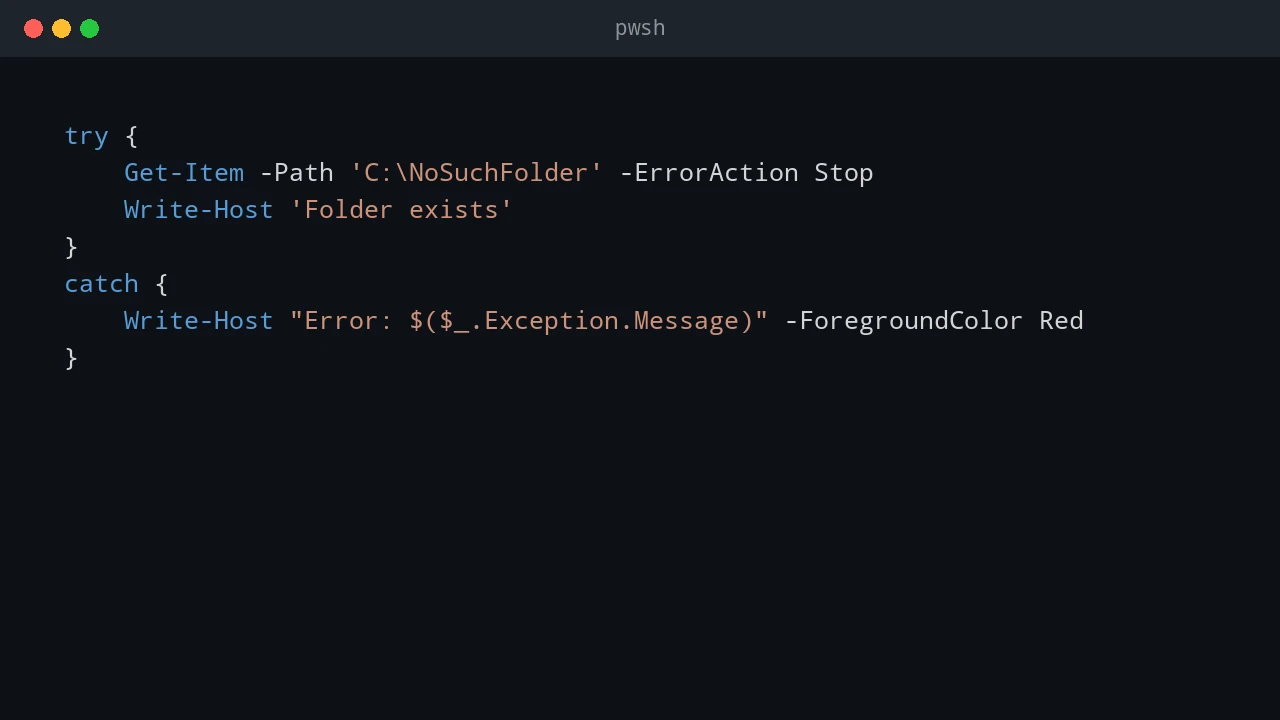
How to handle PowerShell errors with try, catch, and finally while writing error messages to both the console and a log file.
How to use PowerShell to discover Windows PCs, query installed applications remotely, and export a software inventory report.
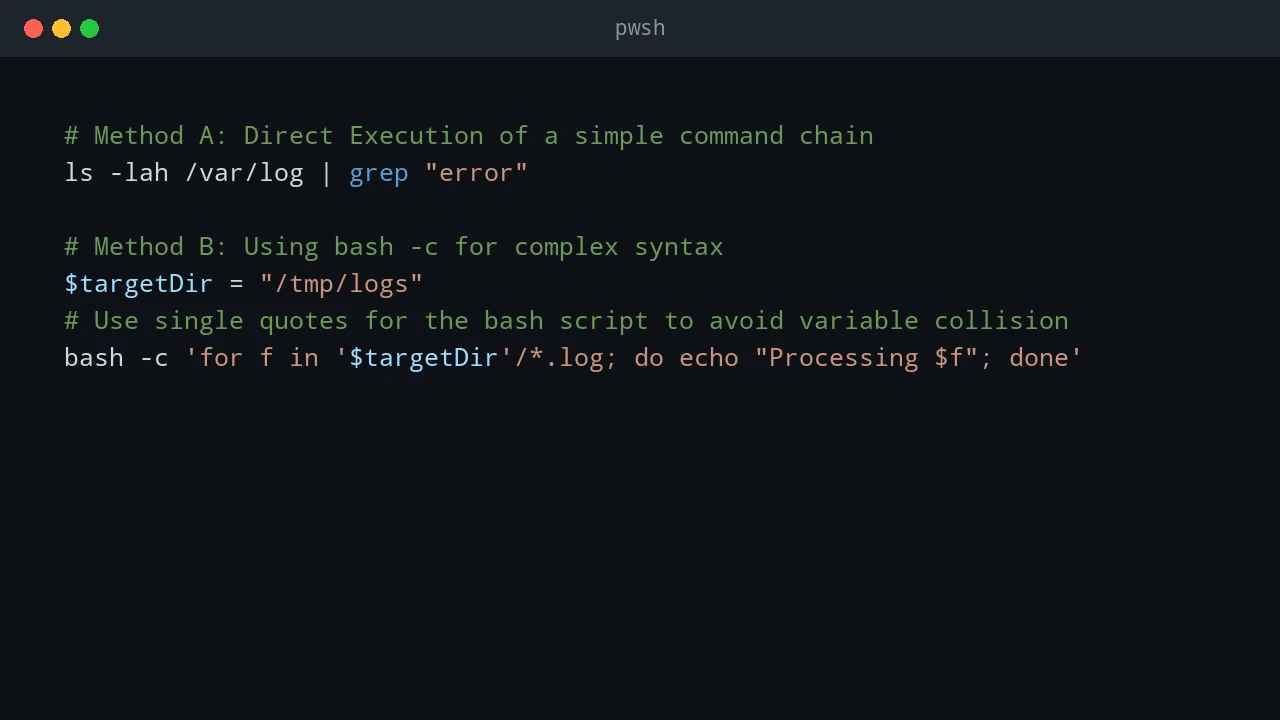
How to use PowerShell with Bash, CMD, JSON, and WSL when working across Windows and Linux.
How to install PowerShell and modules on connected machines and offline or restricted networks.
PowerShell security notes for elevation, Windows Defender Firewall rules, and safely unblocking downloaded files.
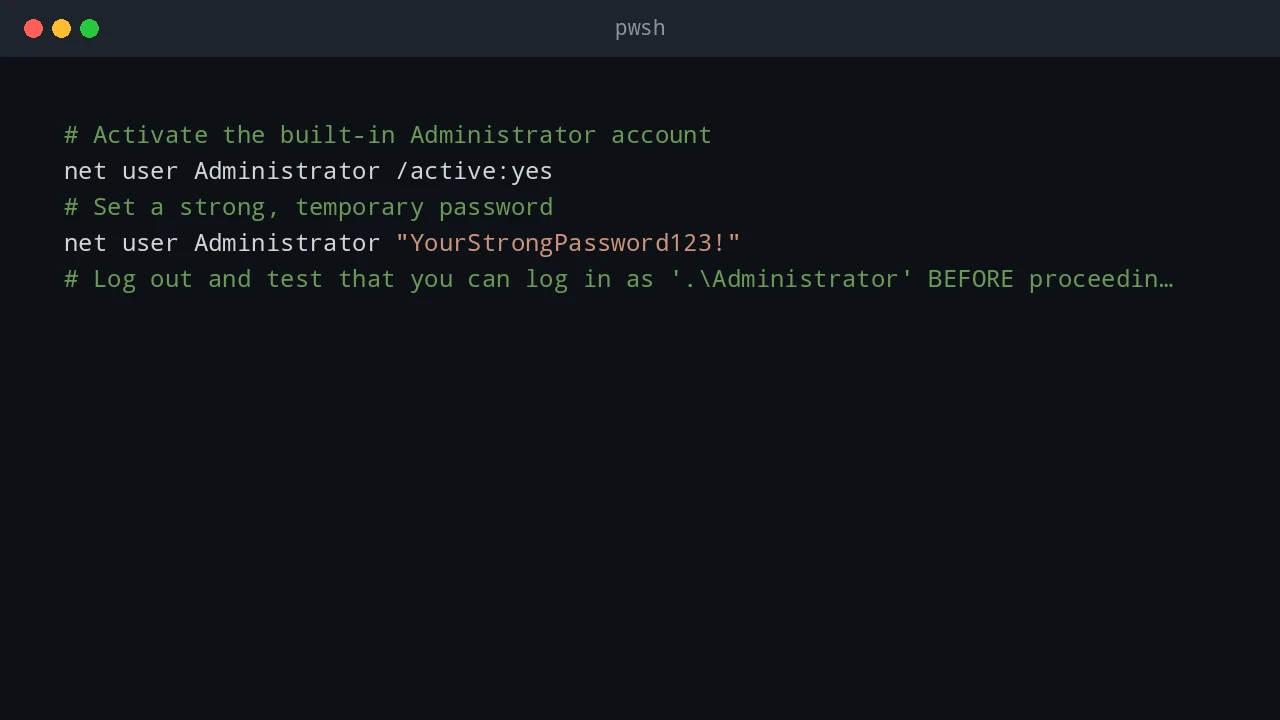
PowerShell notes for Office deployment, Office activation firewall rules, Get-ADUser queries, and domain rejoin troubleshooting.
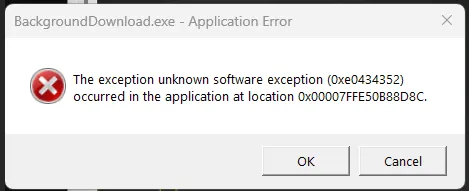
Troubleshooting notes for Windows network share errors, WSL crashes, VMware TPM checks, and disk space problems.