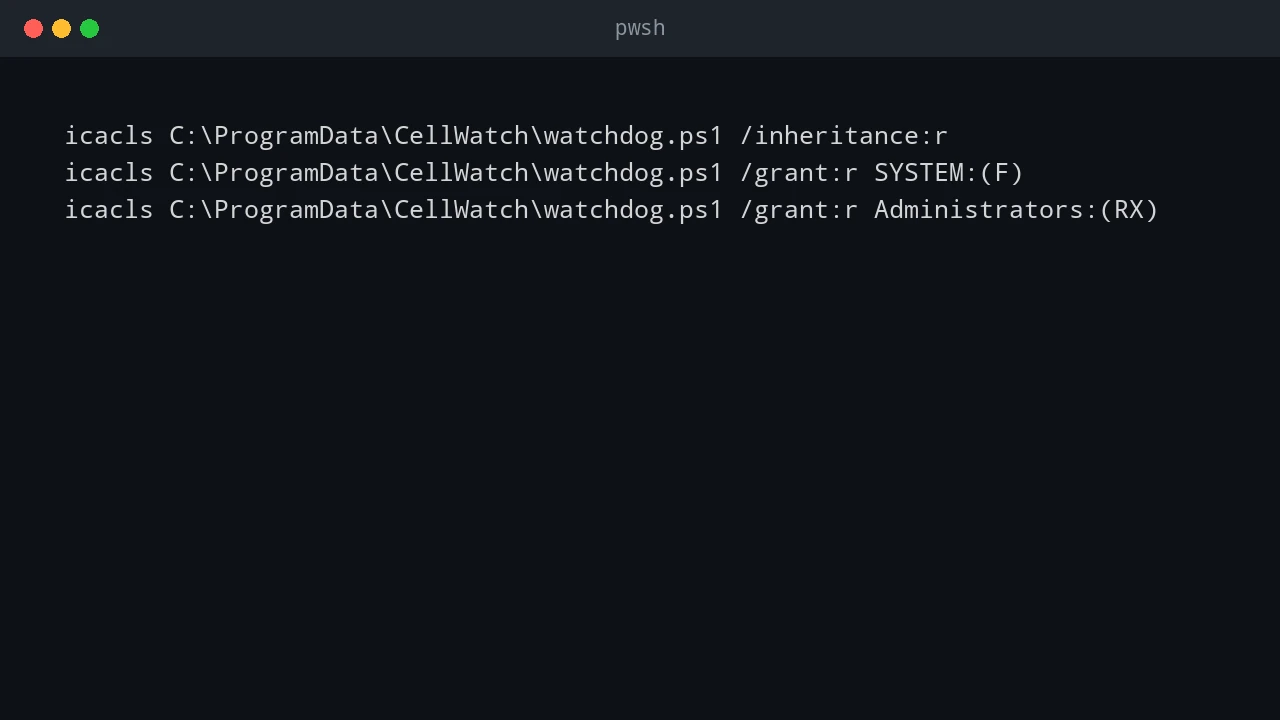
Protecting a PowerShell Watchdog Script from Tampering
A scheduled PowerShell script running as SYSTEM is a high-value target. Lock it down with NTFS ACLs, code signing, auditing, and central deployment.
A scheduled PowerShell script running as SYSTEM is a high-value target. Lock it down with NTFS ACLs, code signing, auditing, and central deployment.
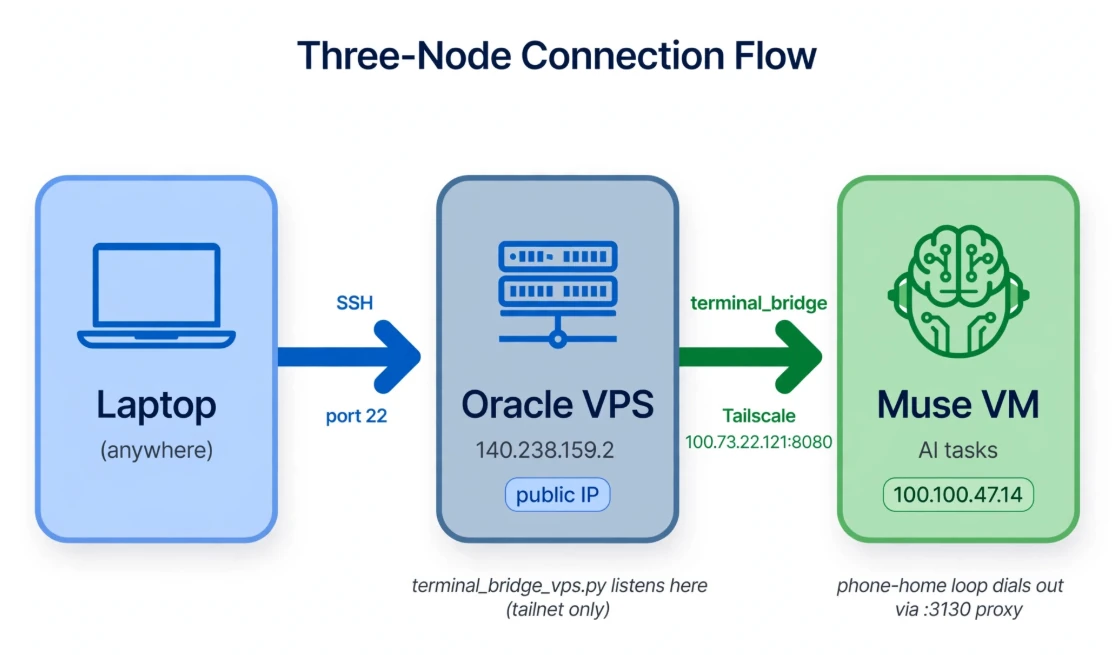
A Tailscale terminal-access postmortem: separate control-plane failures from SSH, trace TCP resets, and choose an authenticated access path.
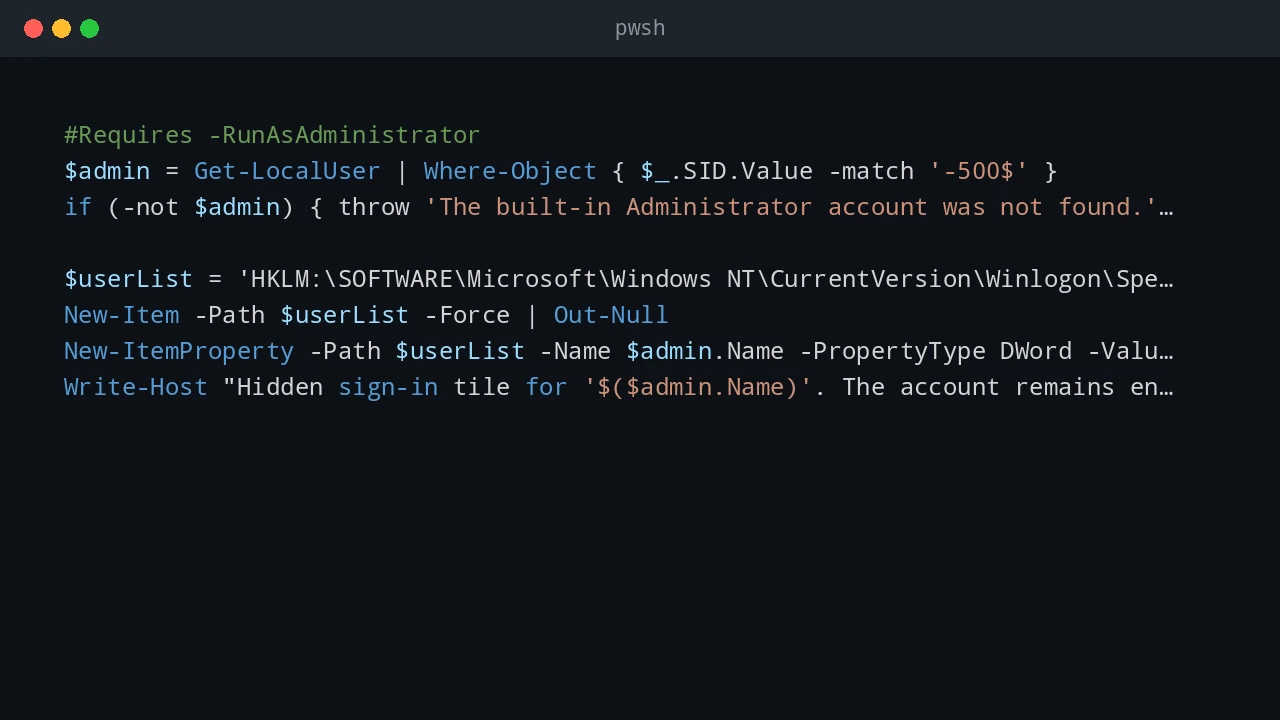
Practical Windows 11 hardening steps for local accounts, network protocols, Remote Desktop, memory integrity, and Defender ASR rules.
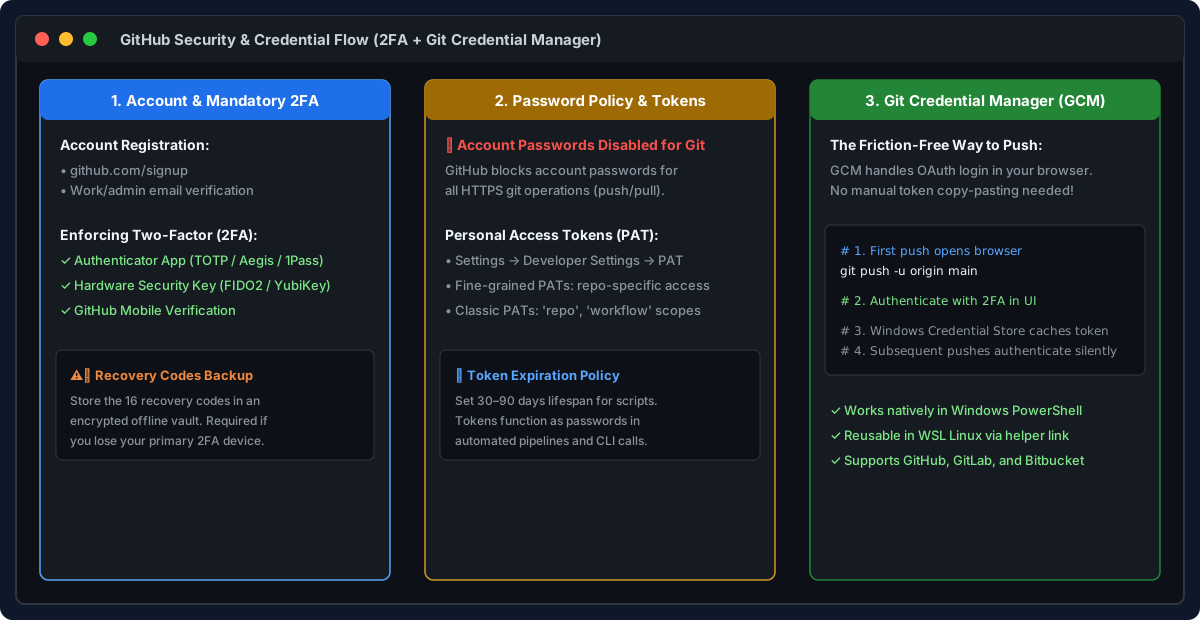
A practical guide to GitHub: registration, mandatory 2FA, token authentication, repositories, projects, gists, cloning, and pull request workflows.
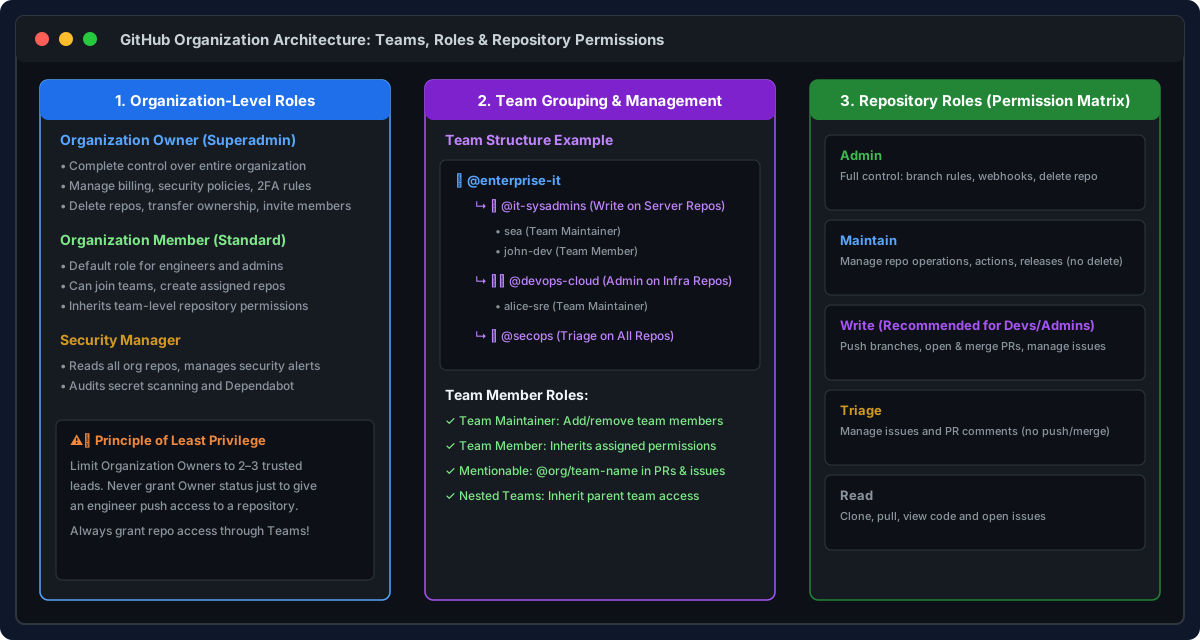
Comprehensive guide to GitHub Organizations and Teams: member roles, granting repository access, branch protection, CODEOWNERS, and Pull Request reviews.
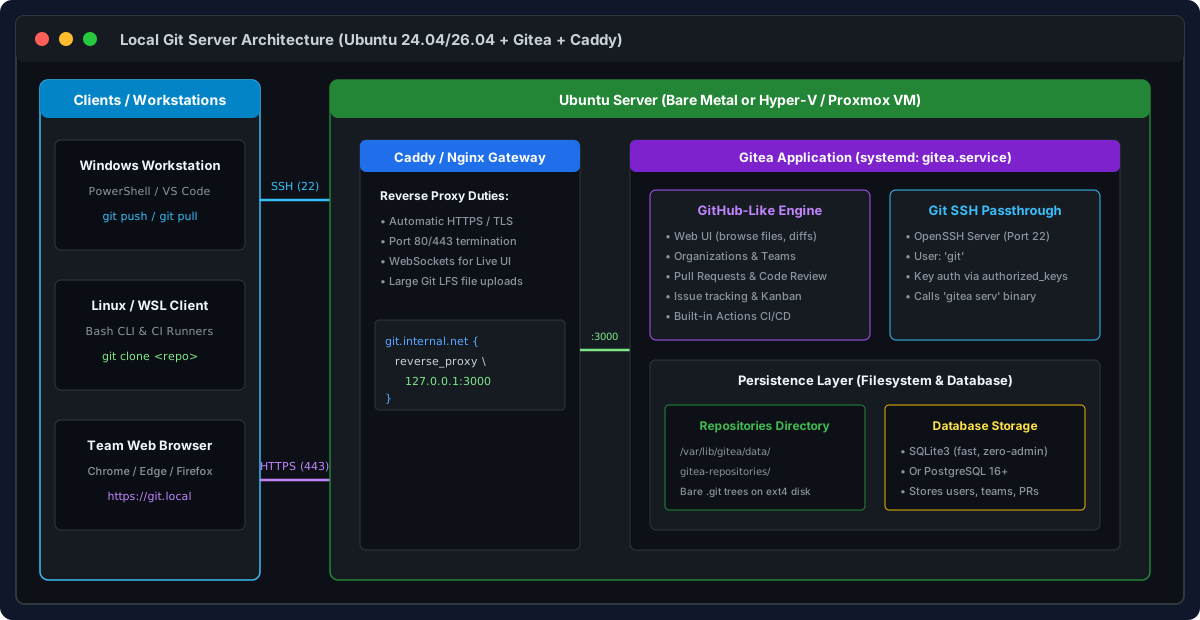
Step-by-step guide to building a self-hosted, GitHub-like Git server on Ubuntu using Gitea, Caddy reverse proxy, SSH passthrough, and team permissions.
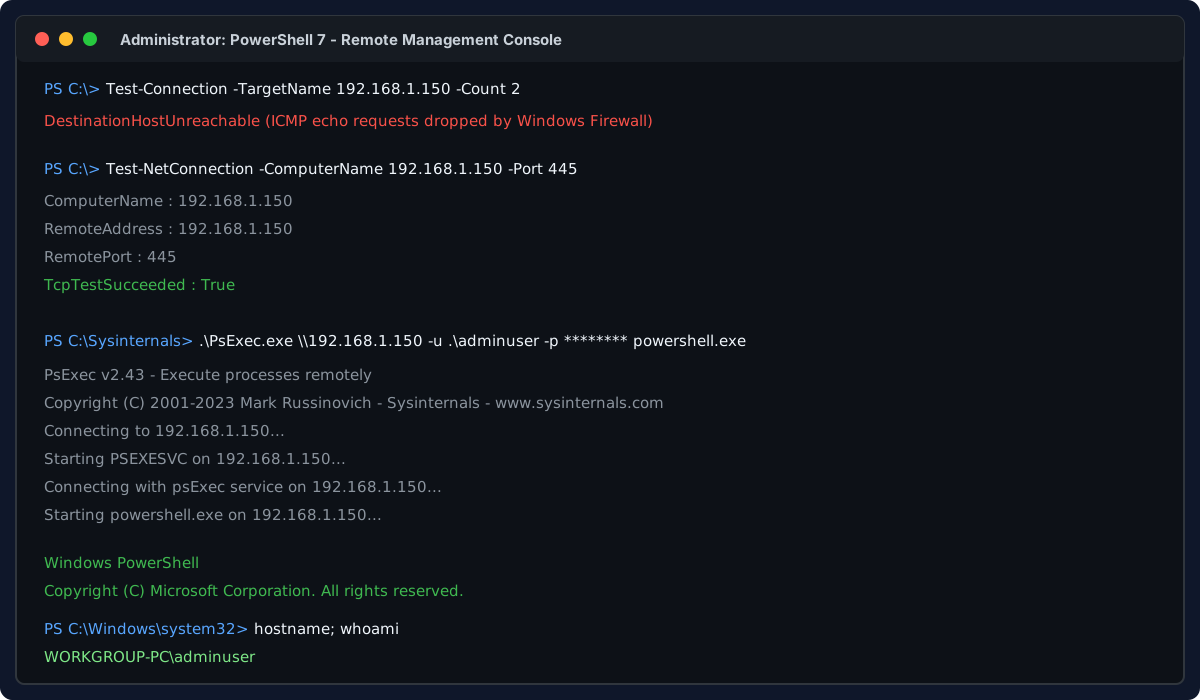
How to gain remote access to an unpingable non-domain Windows computer with zero console or physical access, using only its IP, local admin credentials, and PsExec to enable RDP, WinRM, and OpenSSH.
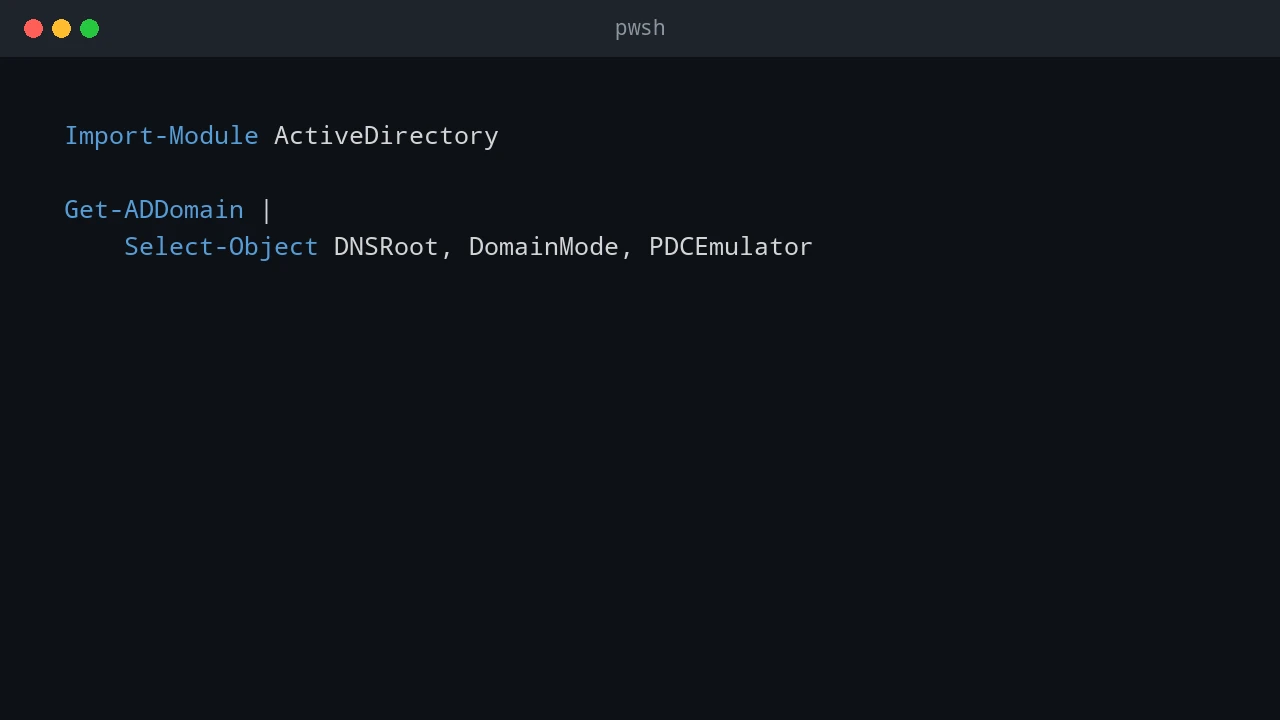
Use an admin workstation, RSAT, PowerShell, Microsoft diagnostics, and Sysinternals AD Explorer to manage Active Directory without routine domain controller logons.
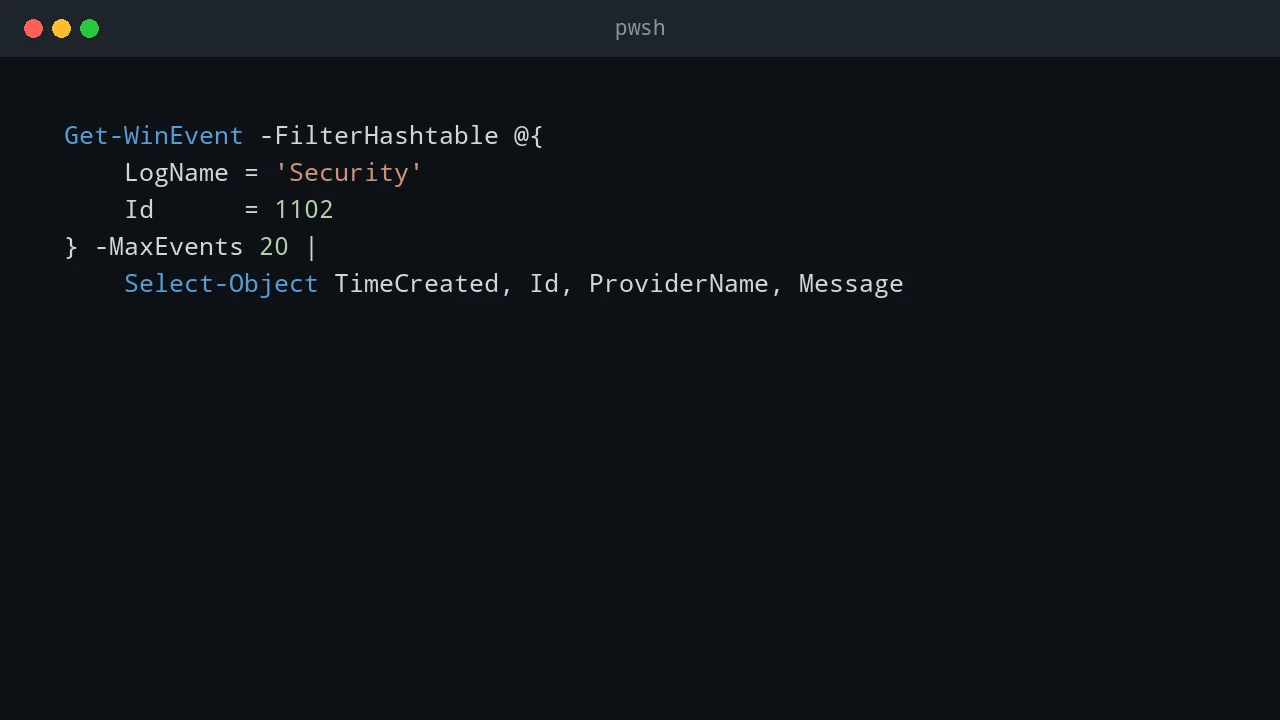
Defensive notes on Windows event log tampering, audit risk, detection signals, and practical controls for administrators.
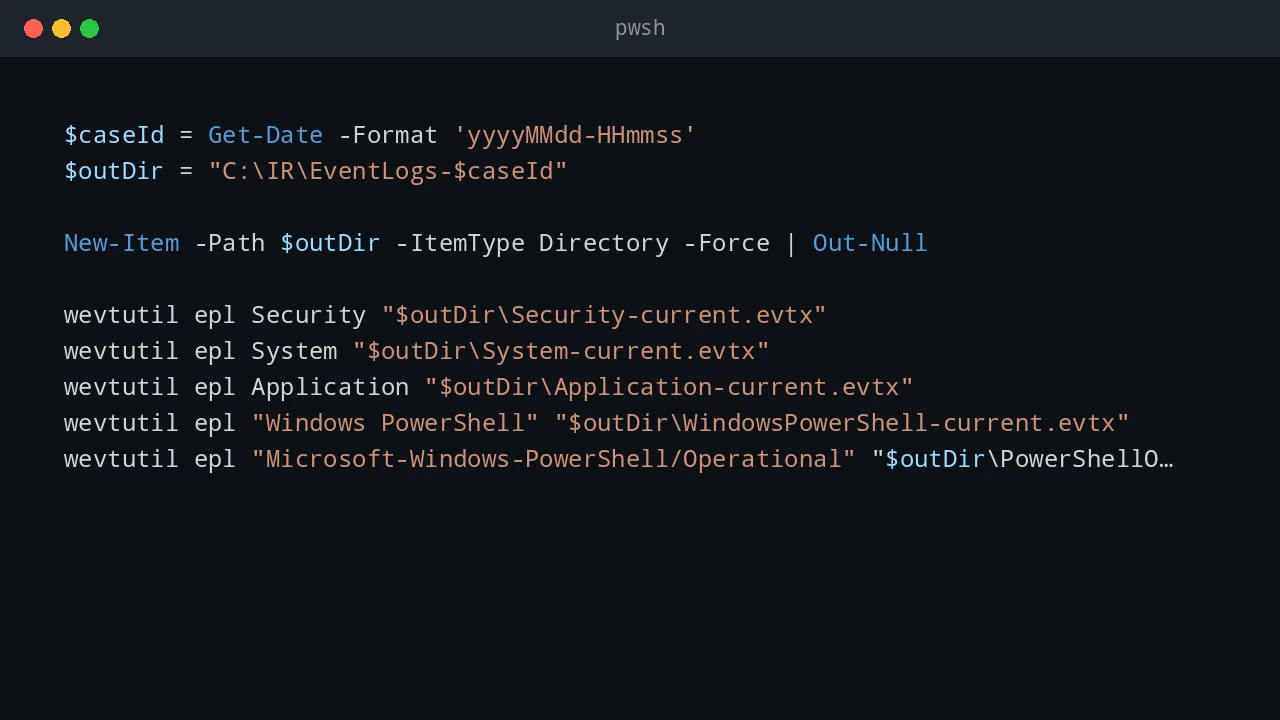
What administrators can recover after Windows event logs are cleared, and how to prevent local log loss with forwarding, exports, and central collection.